GitOps Secrets Management and Terraform
Matt Gowie (@Gowiem)
+
+
Presented By
- Matt Gowie (@Gowiem on internet)
-
Terraform + AWS Consultant (masterpoint.io
-
Terraform Open Source Maintainer + Instructor
- Into climbing, running, and the outdoors
First: What is "GitOps"?
The core idea of GitOps is having a Git repository that always contains declarative descriptions of the infrastructure currently desired in the production environment and an automated process to make the production environment match the described state in the repository. If you want to deploy a new application or update an existing one, you only need to update the repository - the automated process handles everything else.
The Problem
How do you deal with secrets in this context when it's a well-known best practice to not commit secrets to your git repository?
The Solution
Mozilla's sops
sops is an editor of encrypted files that supports YAML, JSON, ENV, INI and BINARY formats and encrypts with AWS KMS, GCP KMS, Azure Key Vault, age, and PGP
sops stands for Secret Operations
Best explained through a demo!

How do we use it?
Great, now we can store secret values in our repository which follows GitOps principals, but now what? How do we utilize those secrets exactly?
Let's look at another demo!
One last cool thing...
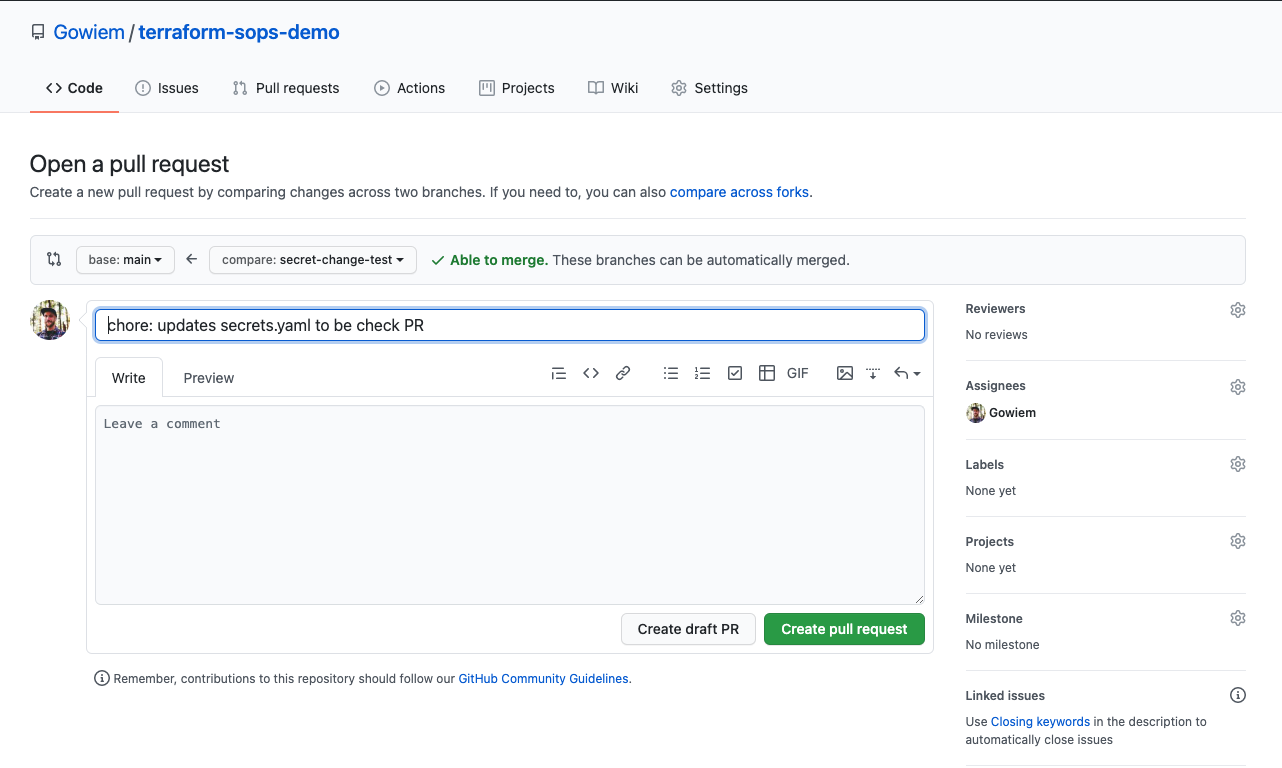
Let's look at changing a secret value and putting that up on PR
References
-
Demo Repo:
https://github.com/Gowiem/terraform-sops-demo
-
GitOps: https://www.gitops.tech/
-
sops: https://github.com/mozilla/sops
- terraform-provider-sops: https://github.com/carlpett/terraform-provider-sops
Thanks folks!
Happy to chat through any questions!
Get in touch: matt@masterpoint.io
https://linkedin.com/in/gowiem