Content ITV PRO
This is Itvedant Content department
Simulate Basic Cloud Attacks and Apply Defensive Measures
Business Scenario
Welcome!
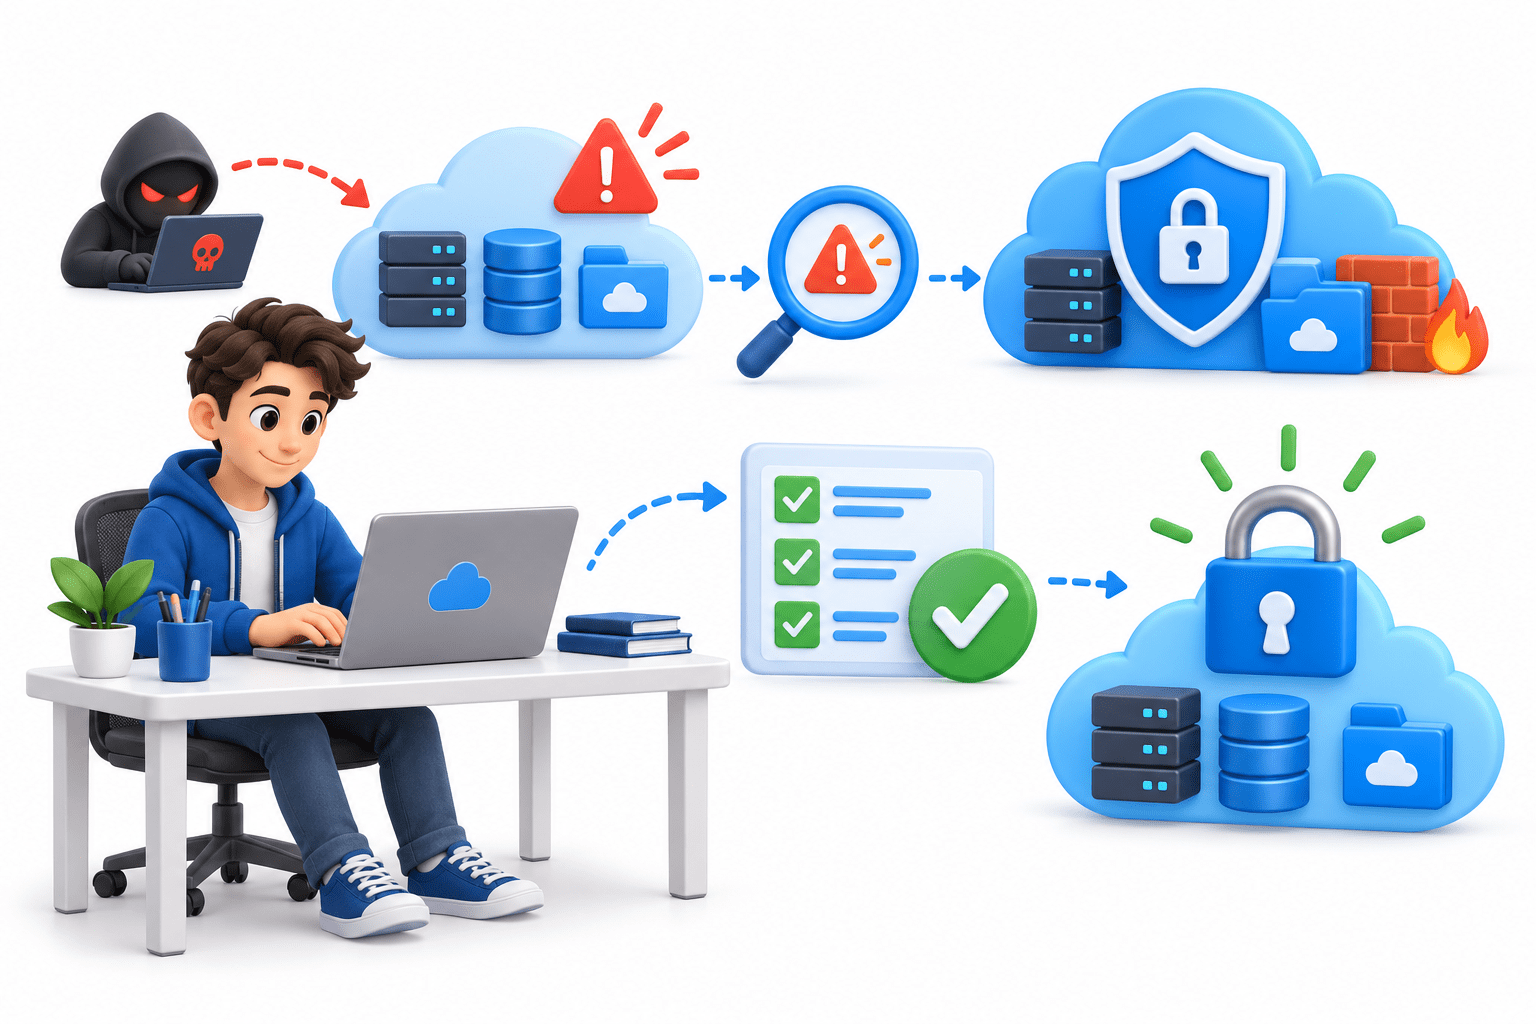
You are a Junior Cloud Security Analyst at CyberSecure Solutions. The organization wants to test whether its cloud environment is protected against common security threats.
Using an authorized training cloud environment, you will simulate basic attacks, identify the security weakness, apply defensive measures, and verify that the attack is no longer successful.
Pre-Lab Preparation
Topic : Cryptography and Cloud Security
1) Cloud Architecture & Web Application Hosting
2) Access Control & Identity Exploitation
3) API Security in Cloud Environments Storage, Data Exposure & Misuse
4) Cloud Attack Simulation & Defense
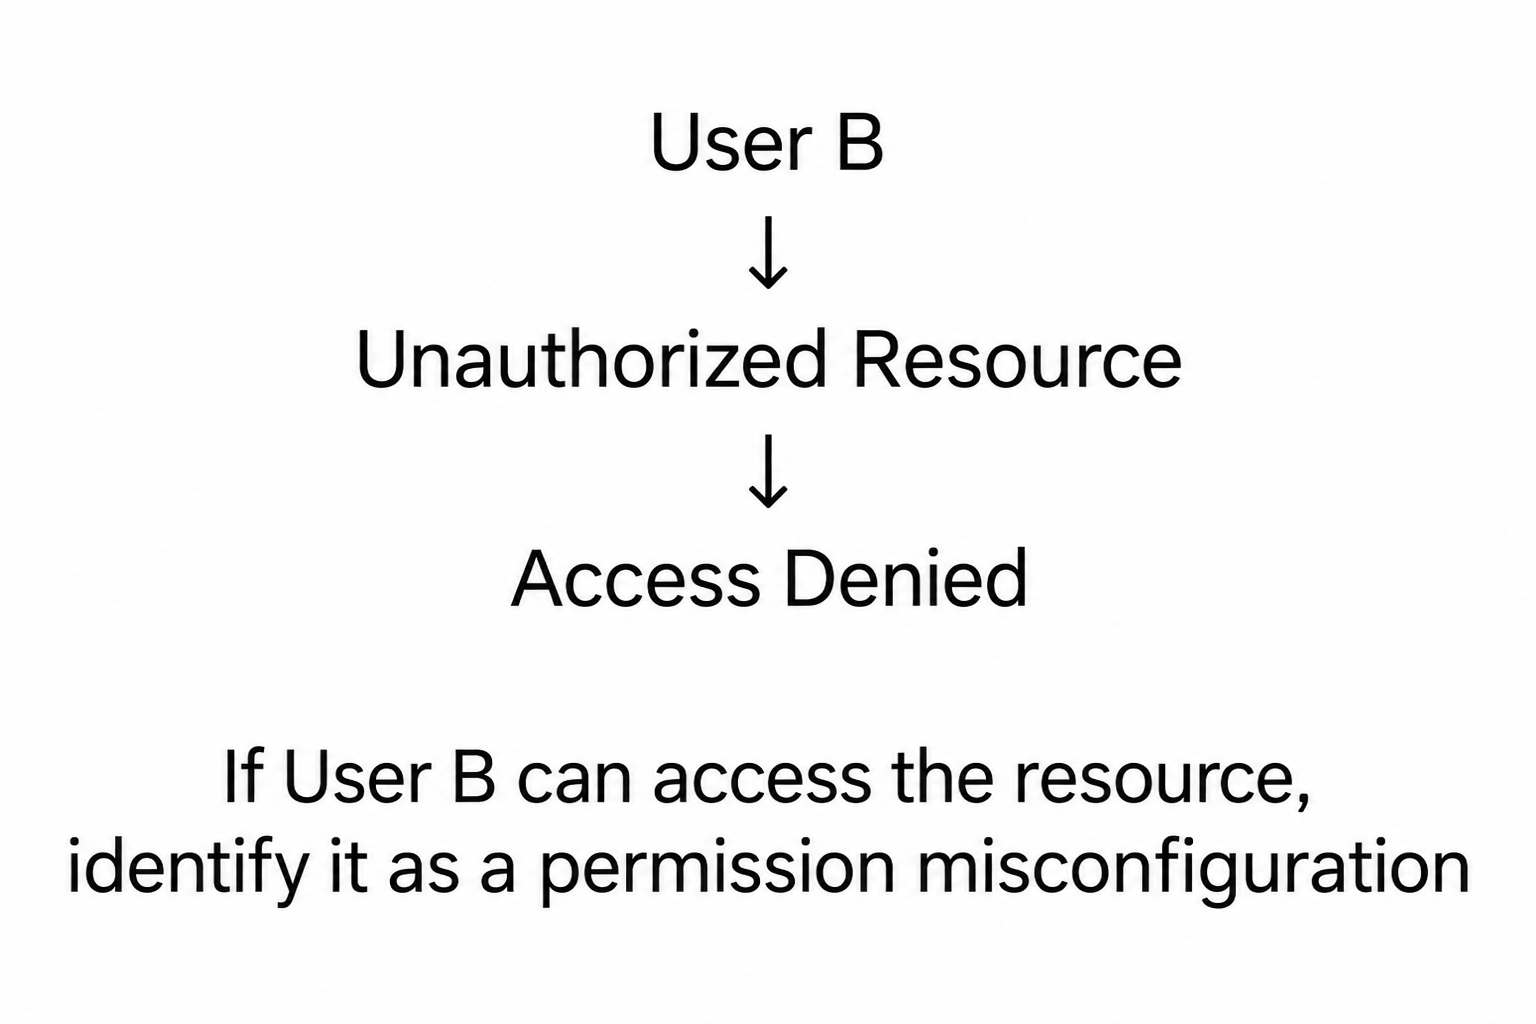
Understand how incorrect permissions can allow unauthorized users to access cloud resources.
1
Create two test users:
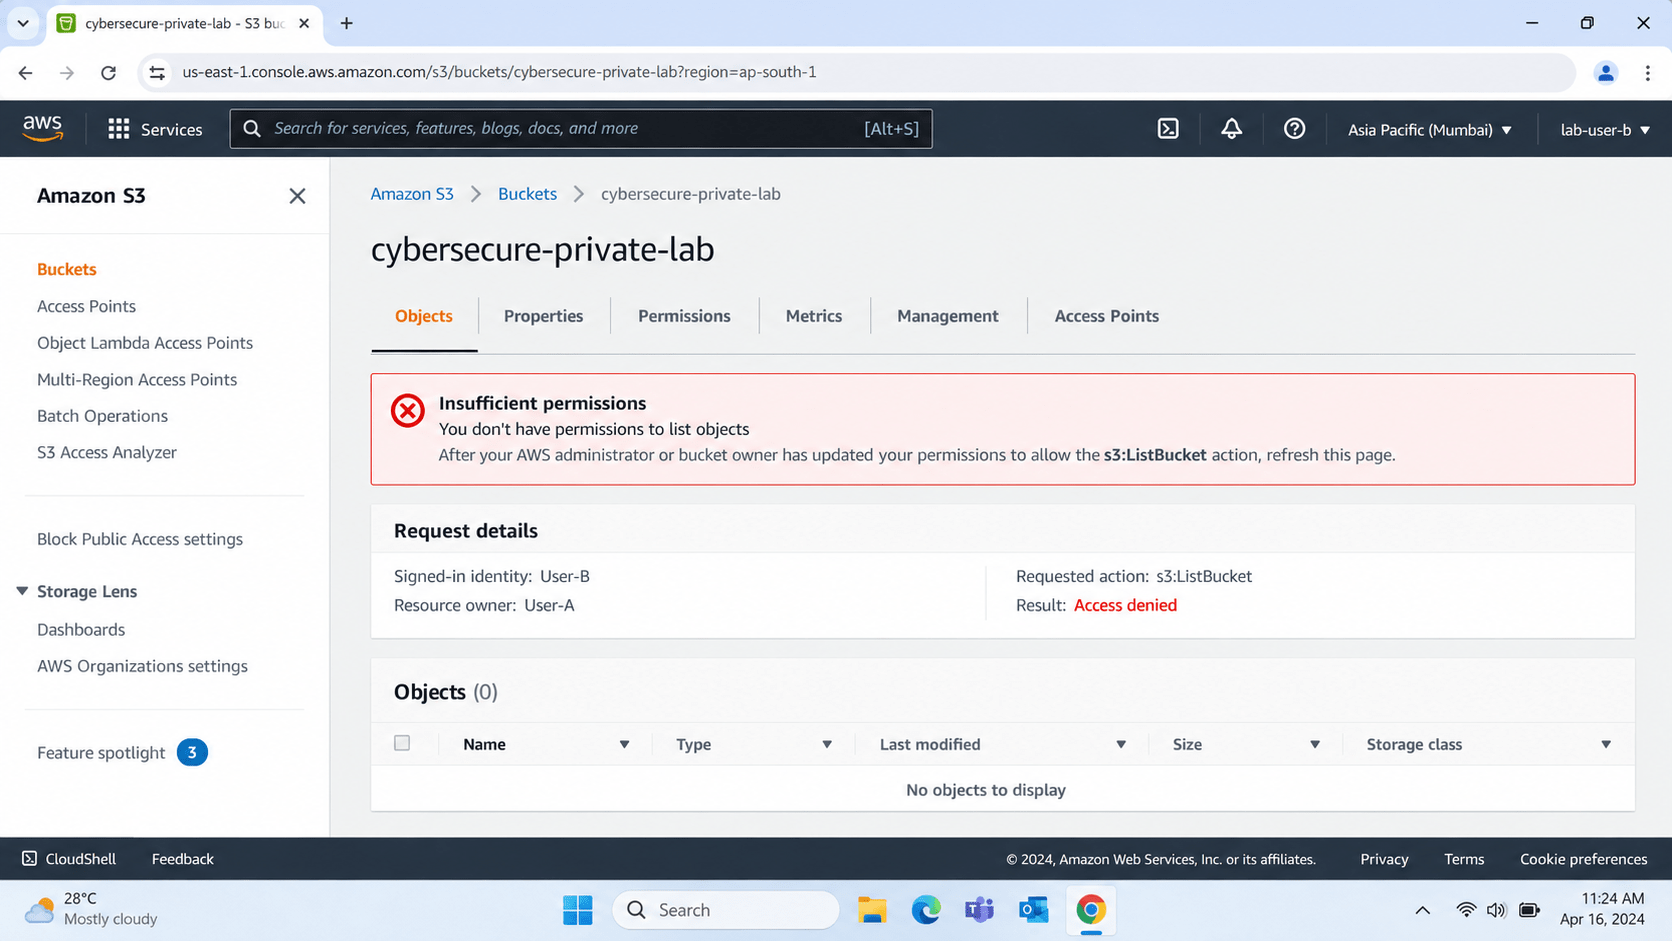
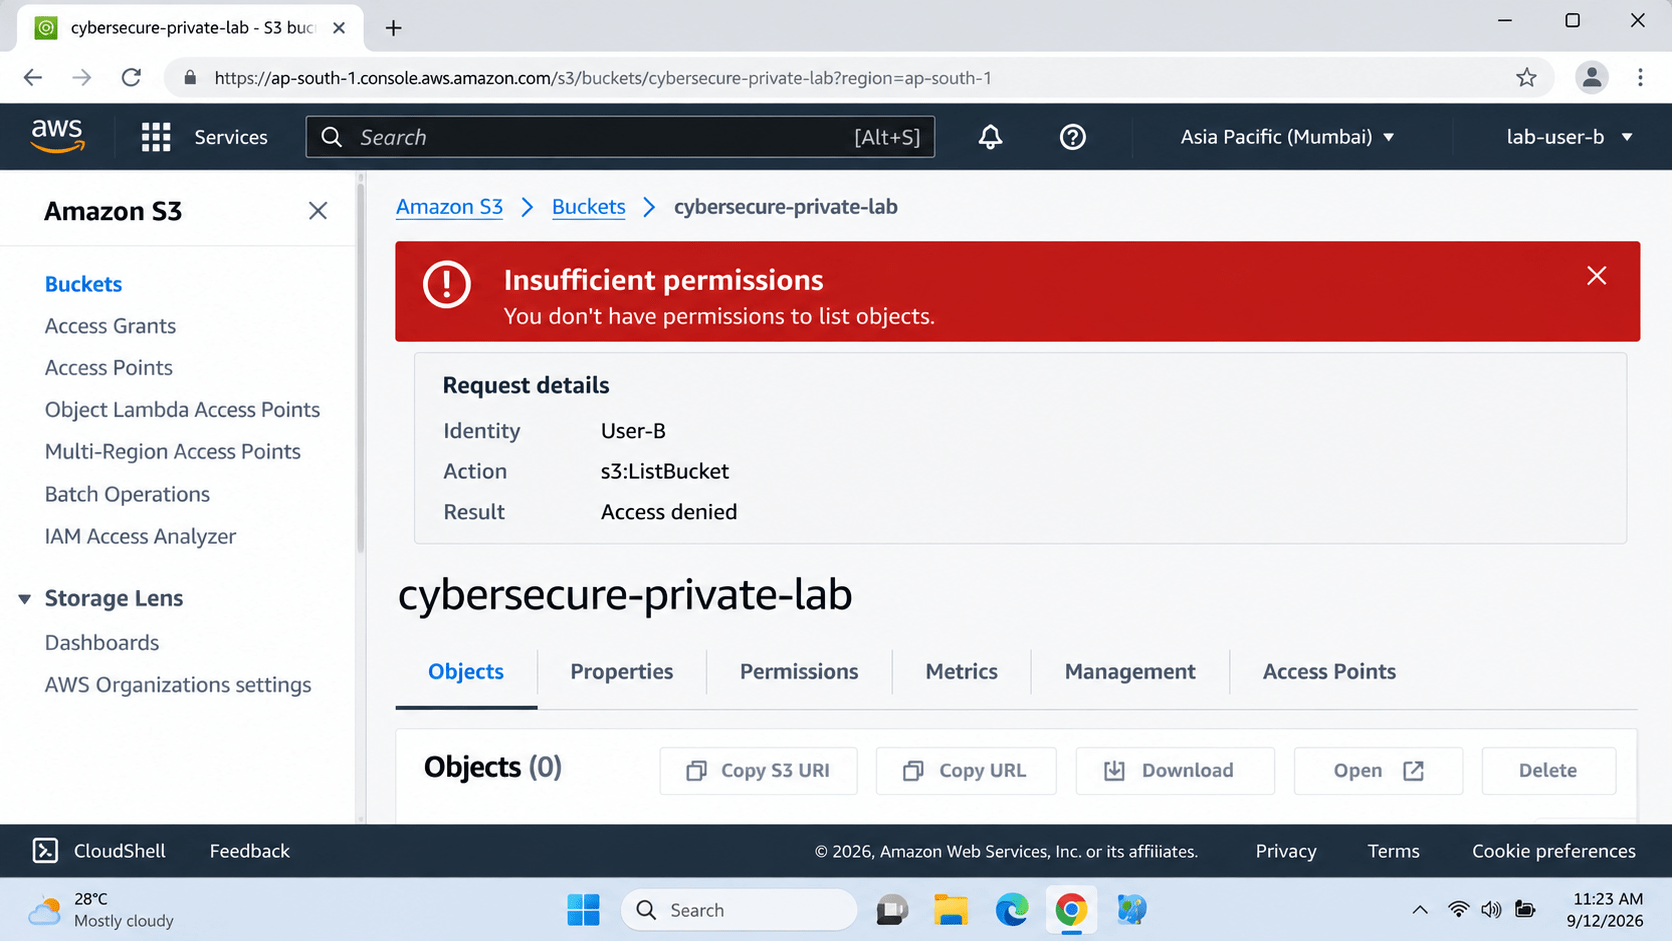
Task 1: Simulate Unauthorized Access
User A
a
User B
b
4
Attempt to access the same resource
2
Give User A access to a test cloud resource
3
Log in as User B
6
Record whether access was allowed or denied
5
Observe the result
Expected Output :-
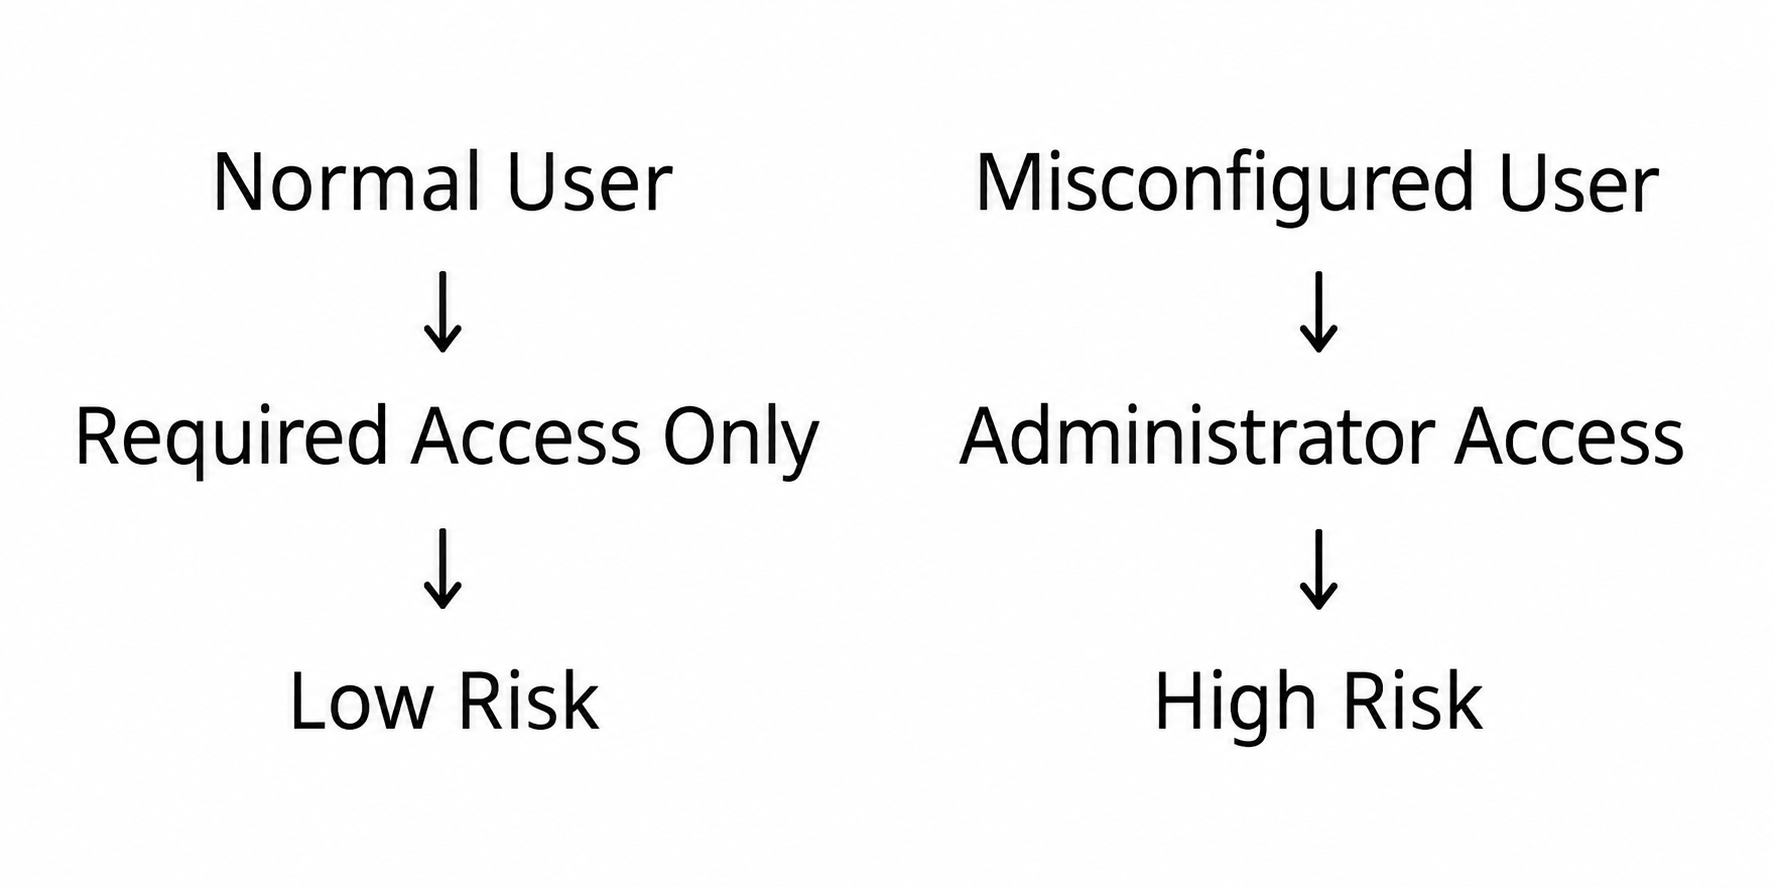
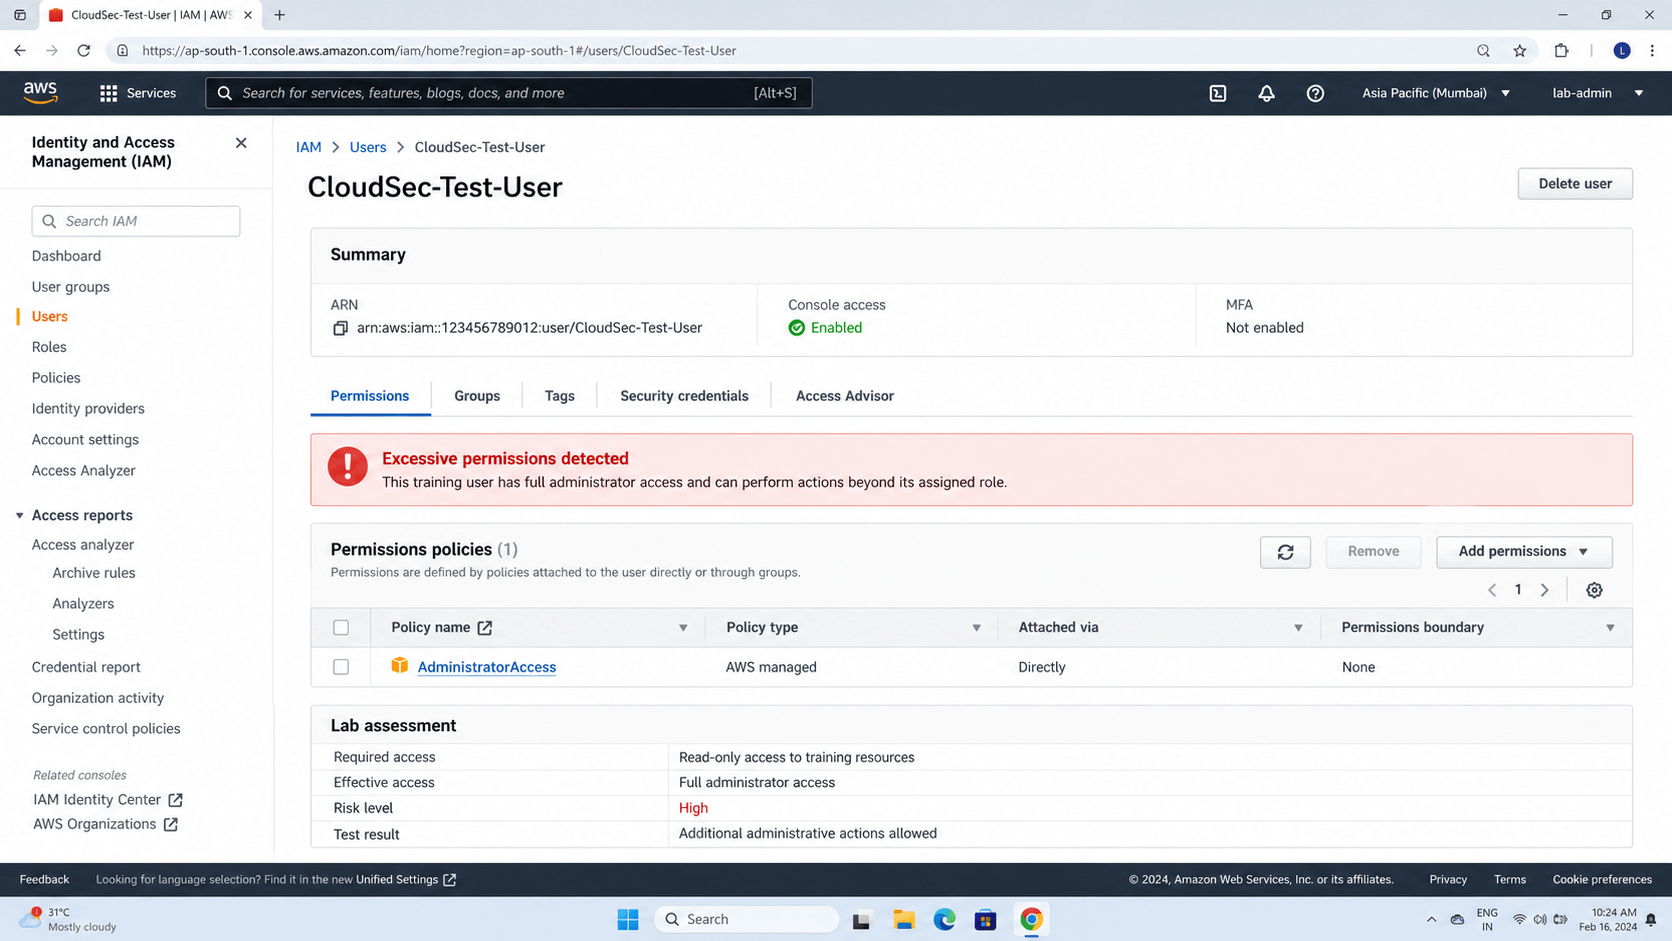
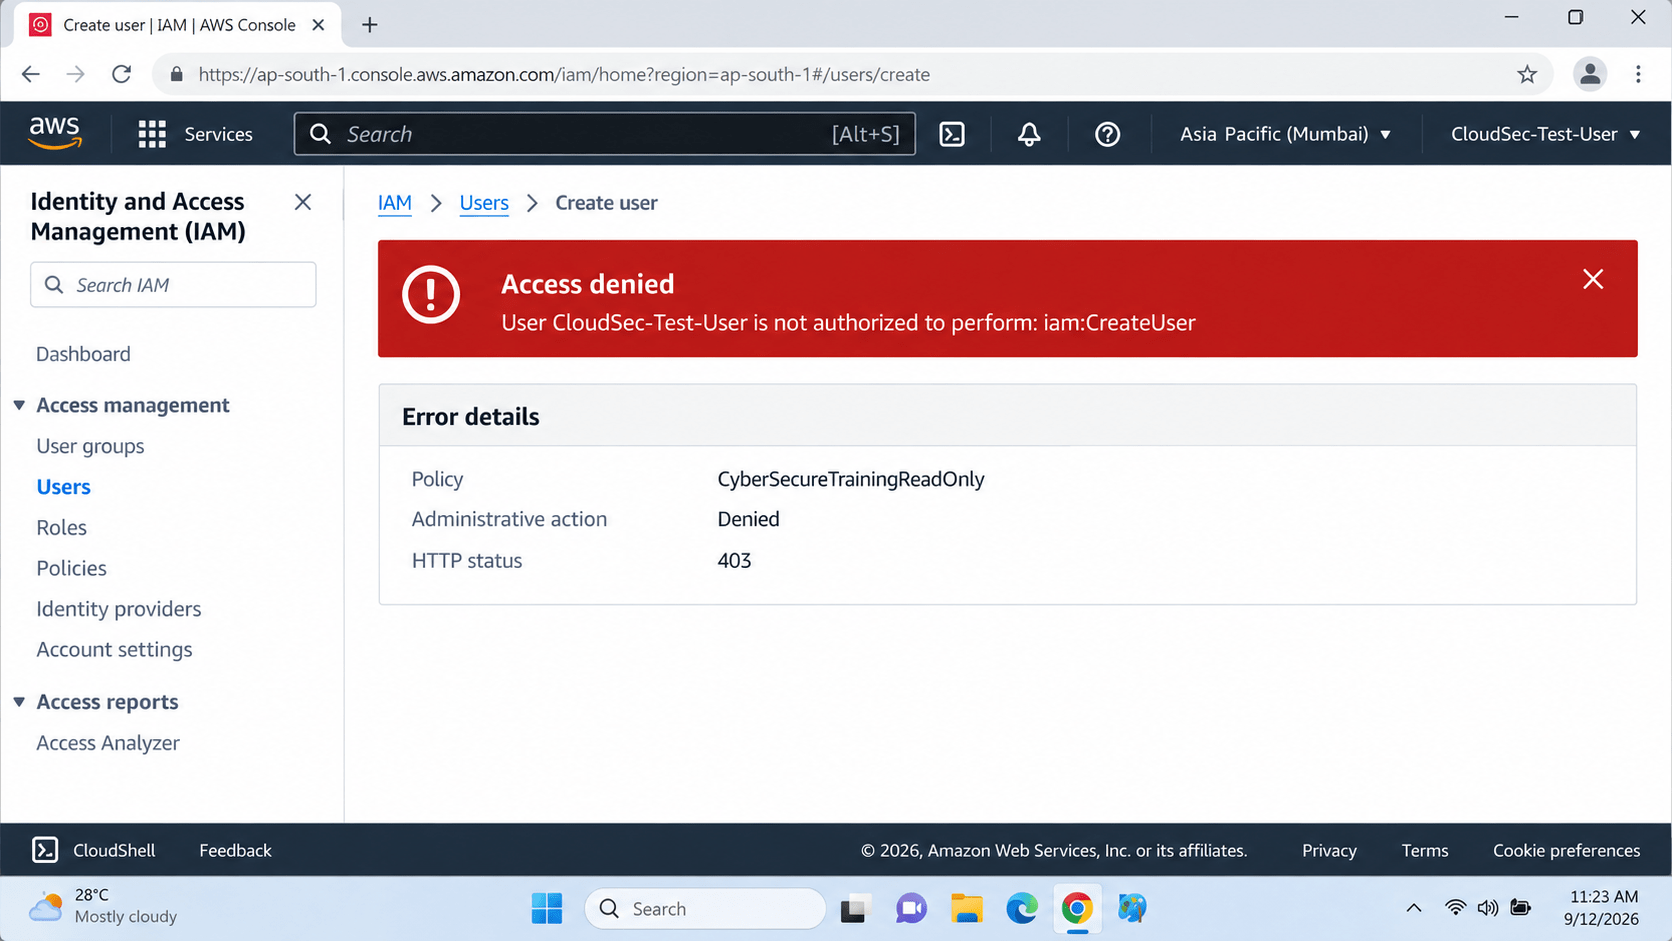
Task 2: Simulate Excessive Privileges
Understand the risk of giving users unnecessary permissions.
1
Select a test IAM user
2
Review the user's permissions
3
Identify unnecessary privileges
4
In the training environment, assign an intentionally excessive permission set
5
Log in as the test user
6
Verify what additional actions the user can perform
7
Record the security risk
Example :
Expected Output :-
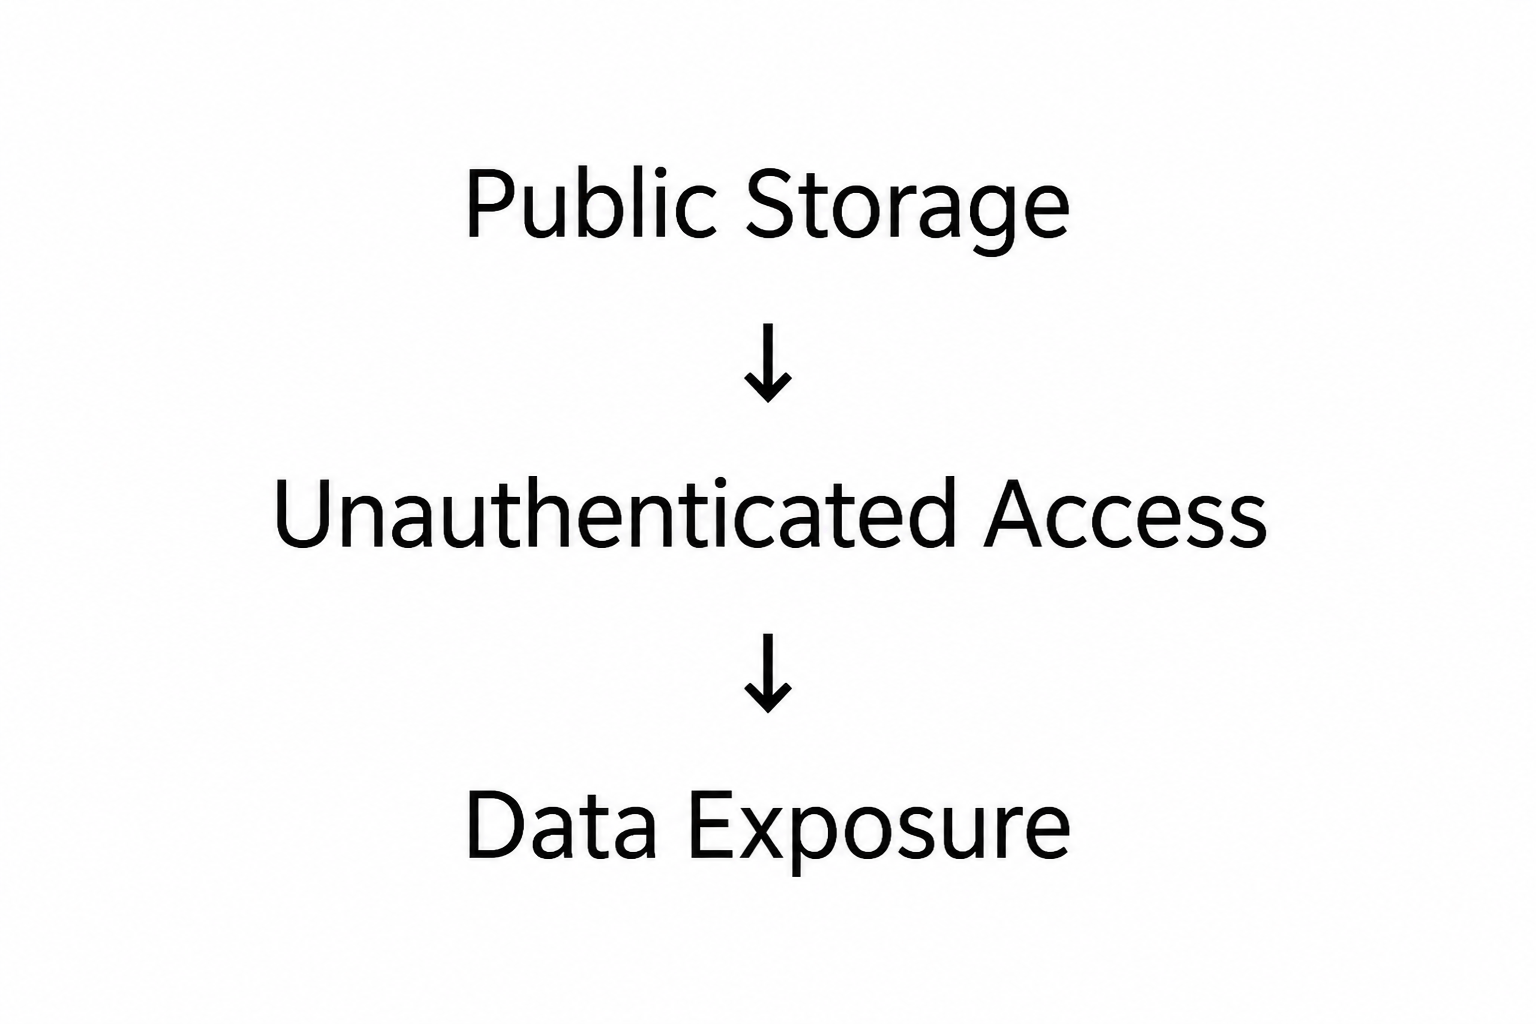
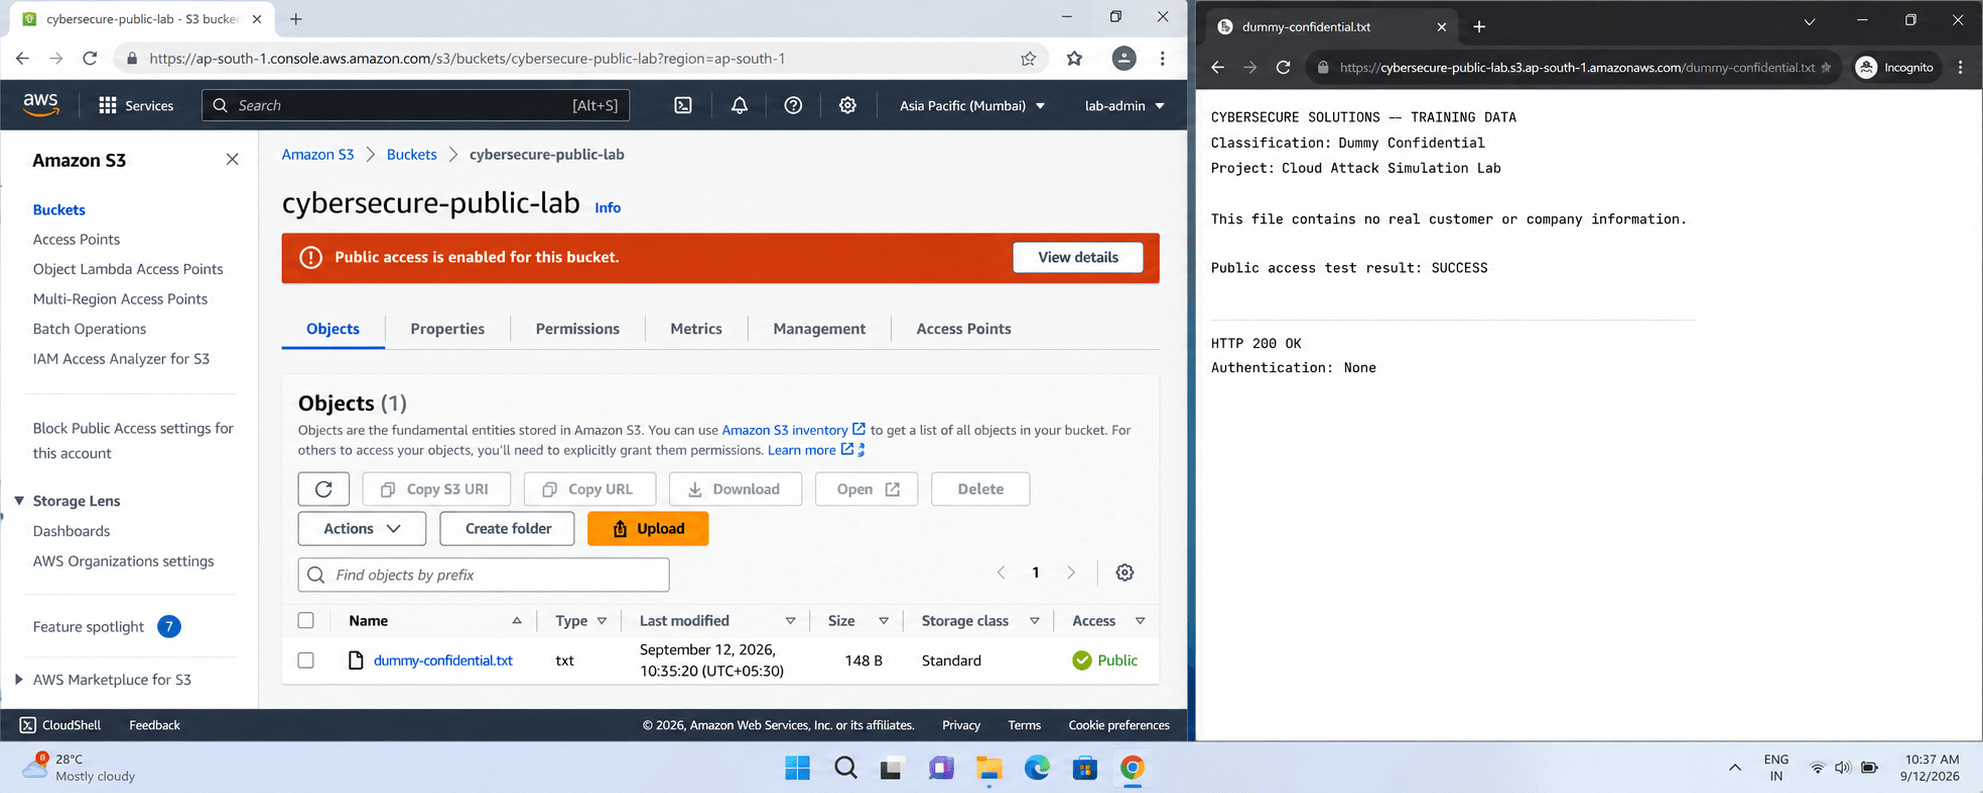
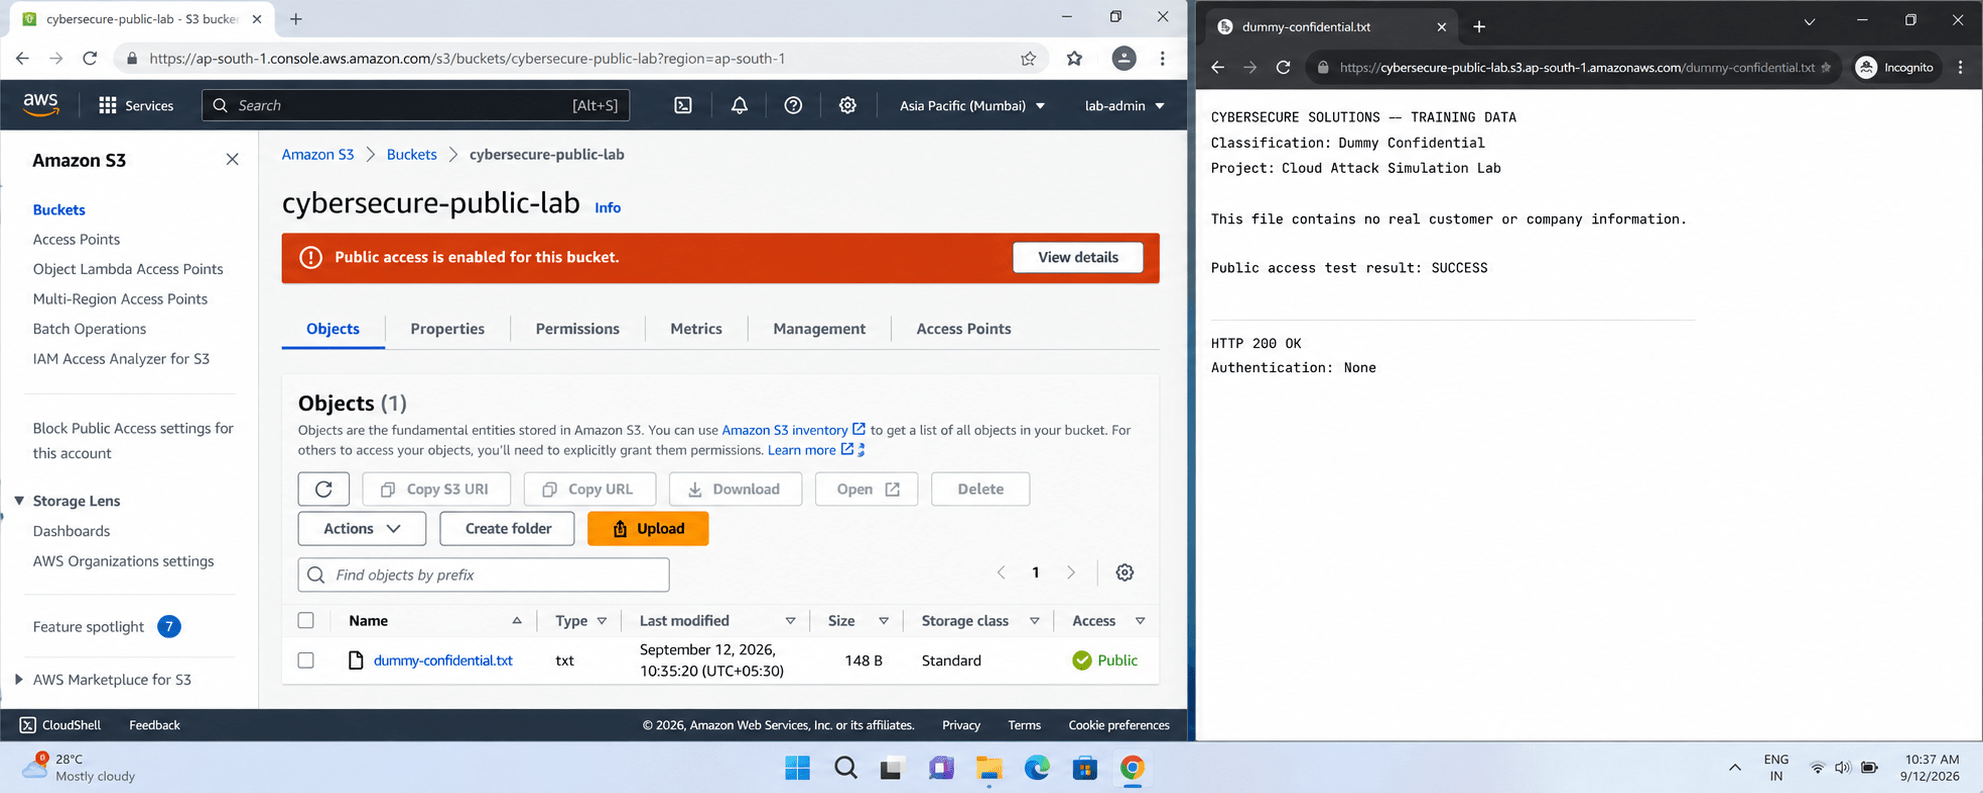
Task 3: Simulate Public Data Exposure
Understand how incorrect cloud storage settings can expose sensitive data
1
Open the assigned test storage bucket/container
2
Place a dummy confidential file inside it
3
Enable public access according to the instructor's lab setup
4
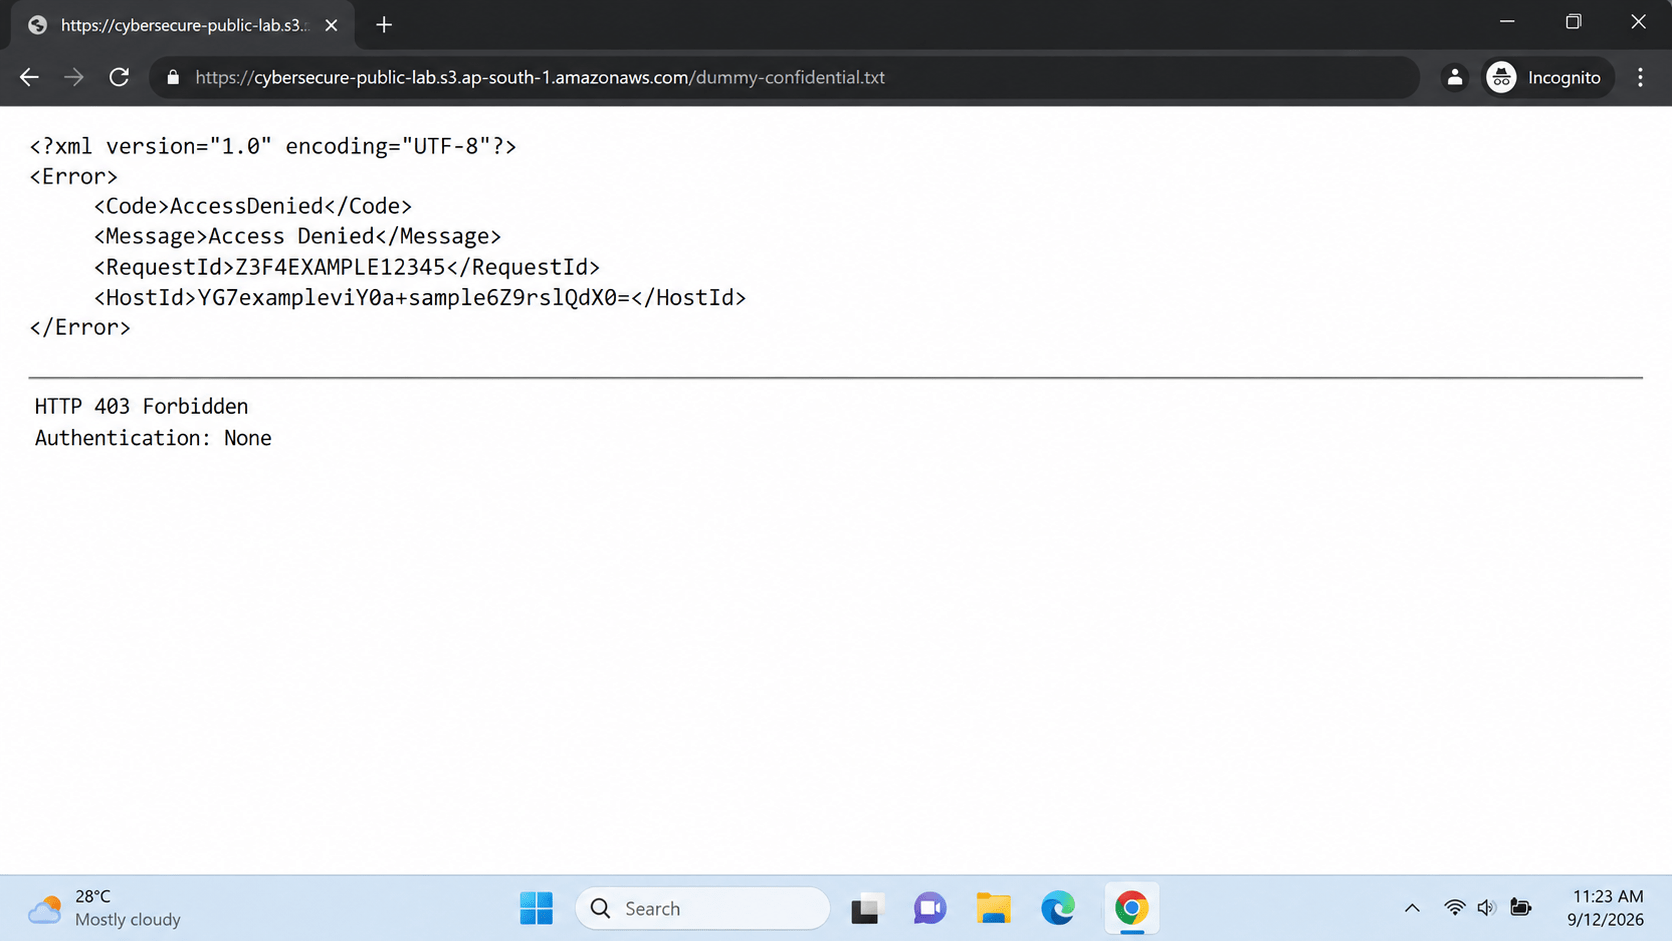
Test whether the file can be accessed without authentication
5
Record the result
6
Do not use real personal or confidential information
Example :
Expected Output :-
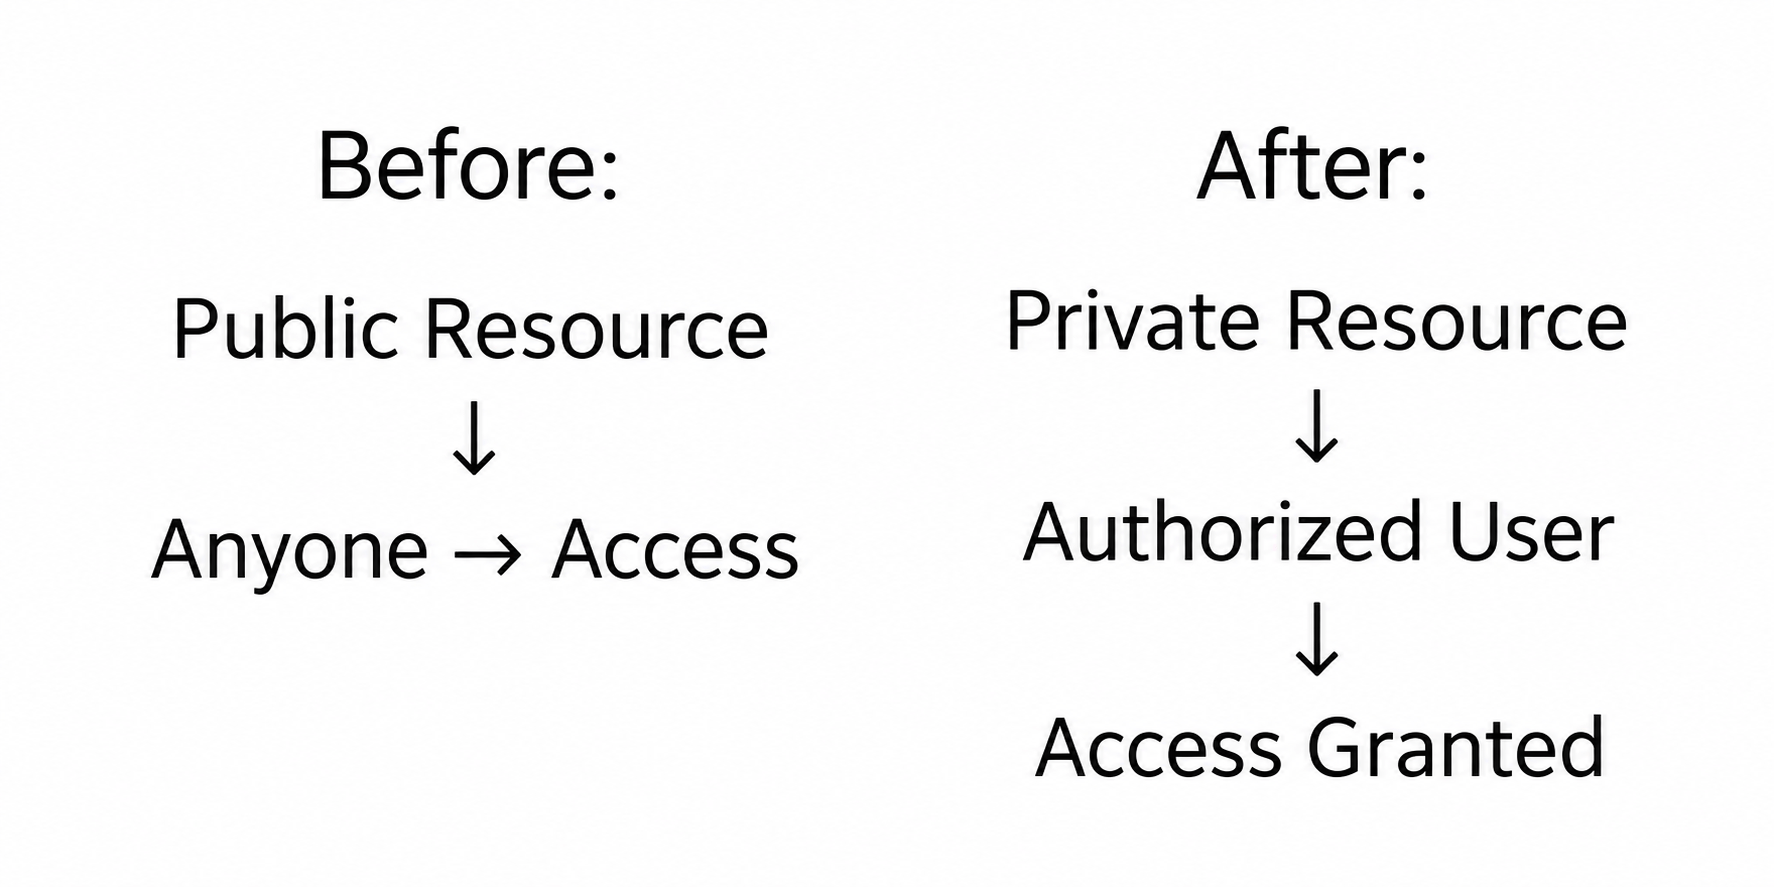
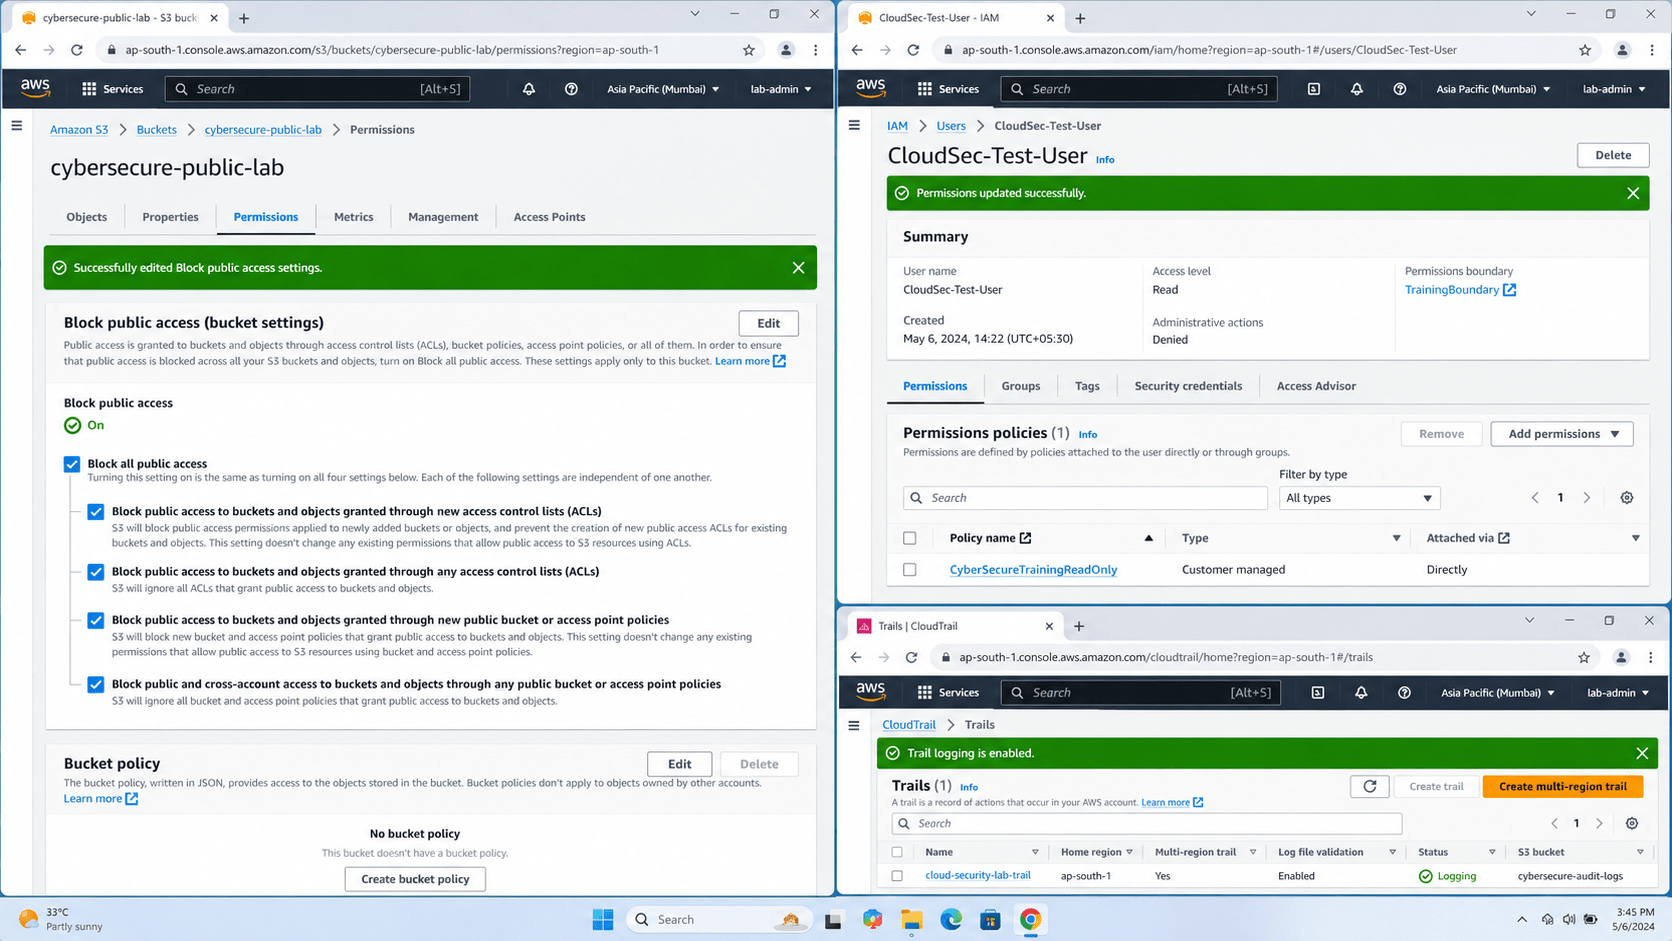
Task 4: Apply Defensive Measures
Correct the identified security weaknesses.
For each simulated attack:
1
Disable unnecessary public access
2
Remove excessive permissions
3
Apply least privilege
4
Ensure only authorized users can access resources
5
Enable appropriate logging and monitoring
6
Save the configuration
Example :
Expected Output :-
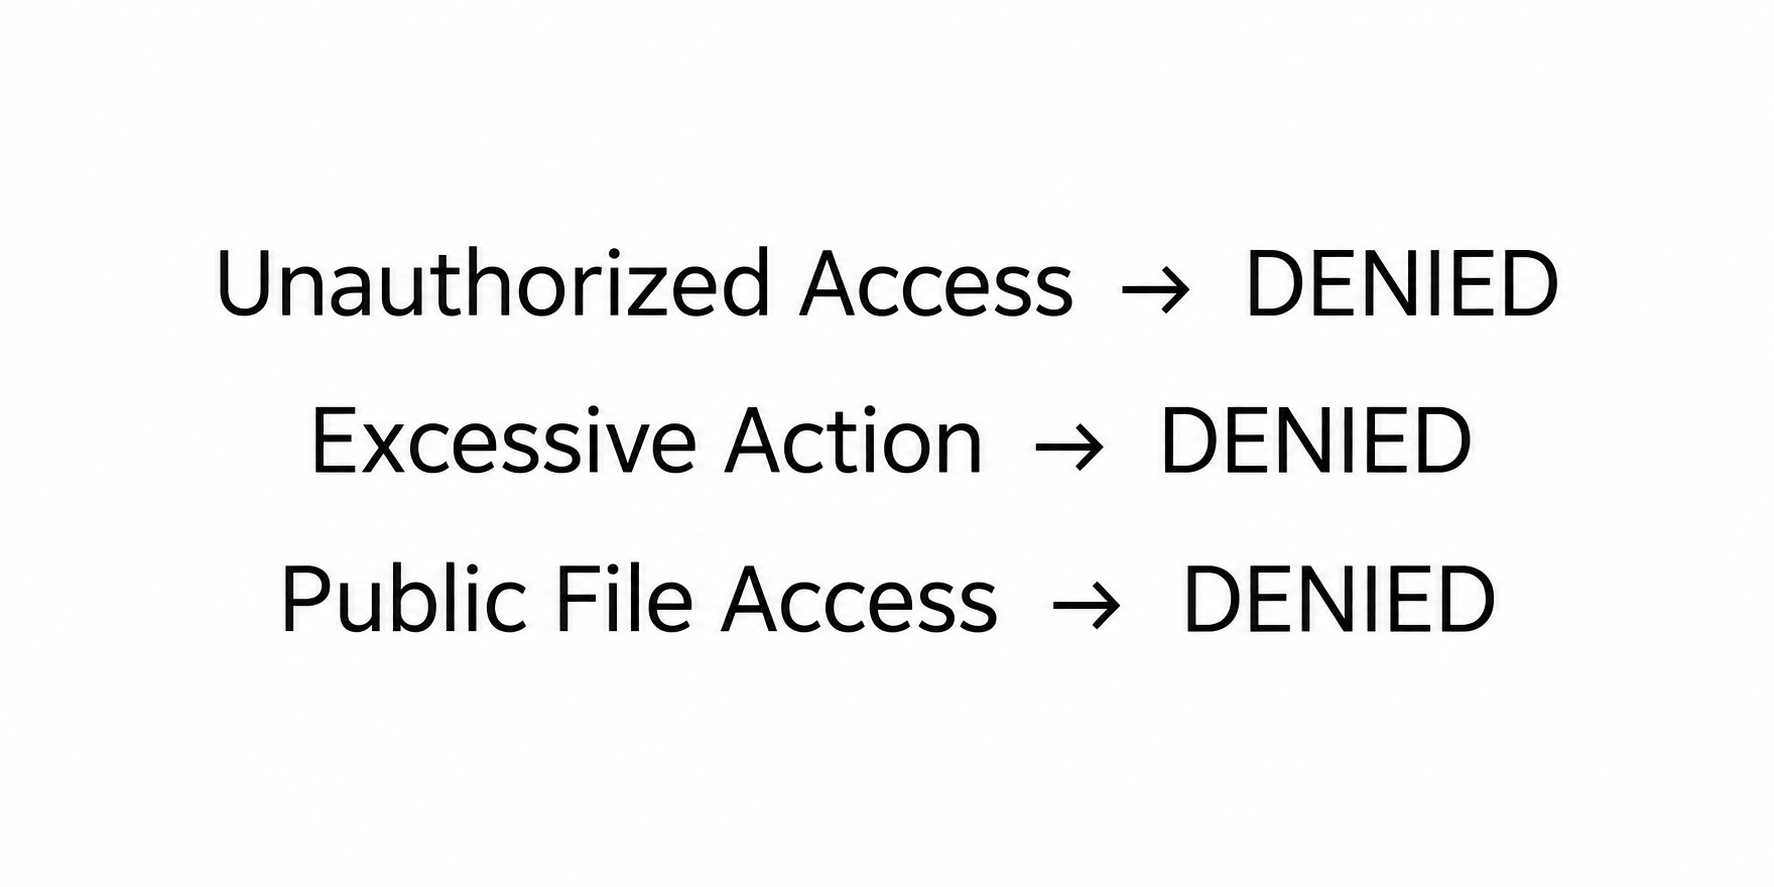
Task 5: Verify the Security Controls
Confirm that the defensive measures work.
1
Log in as the unauthorized test user
2
Attempt to access the protected resource
3
Attempt the previously excessive action
4
Try to access the protected storage object
5
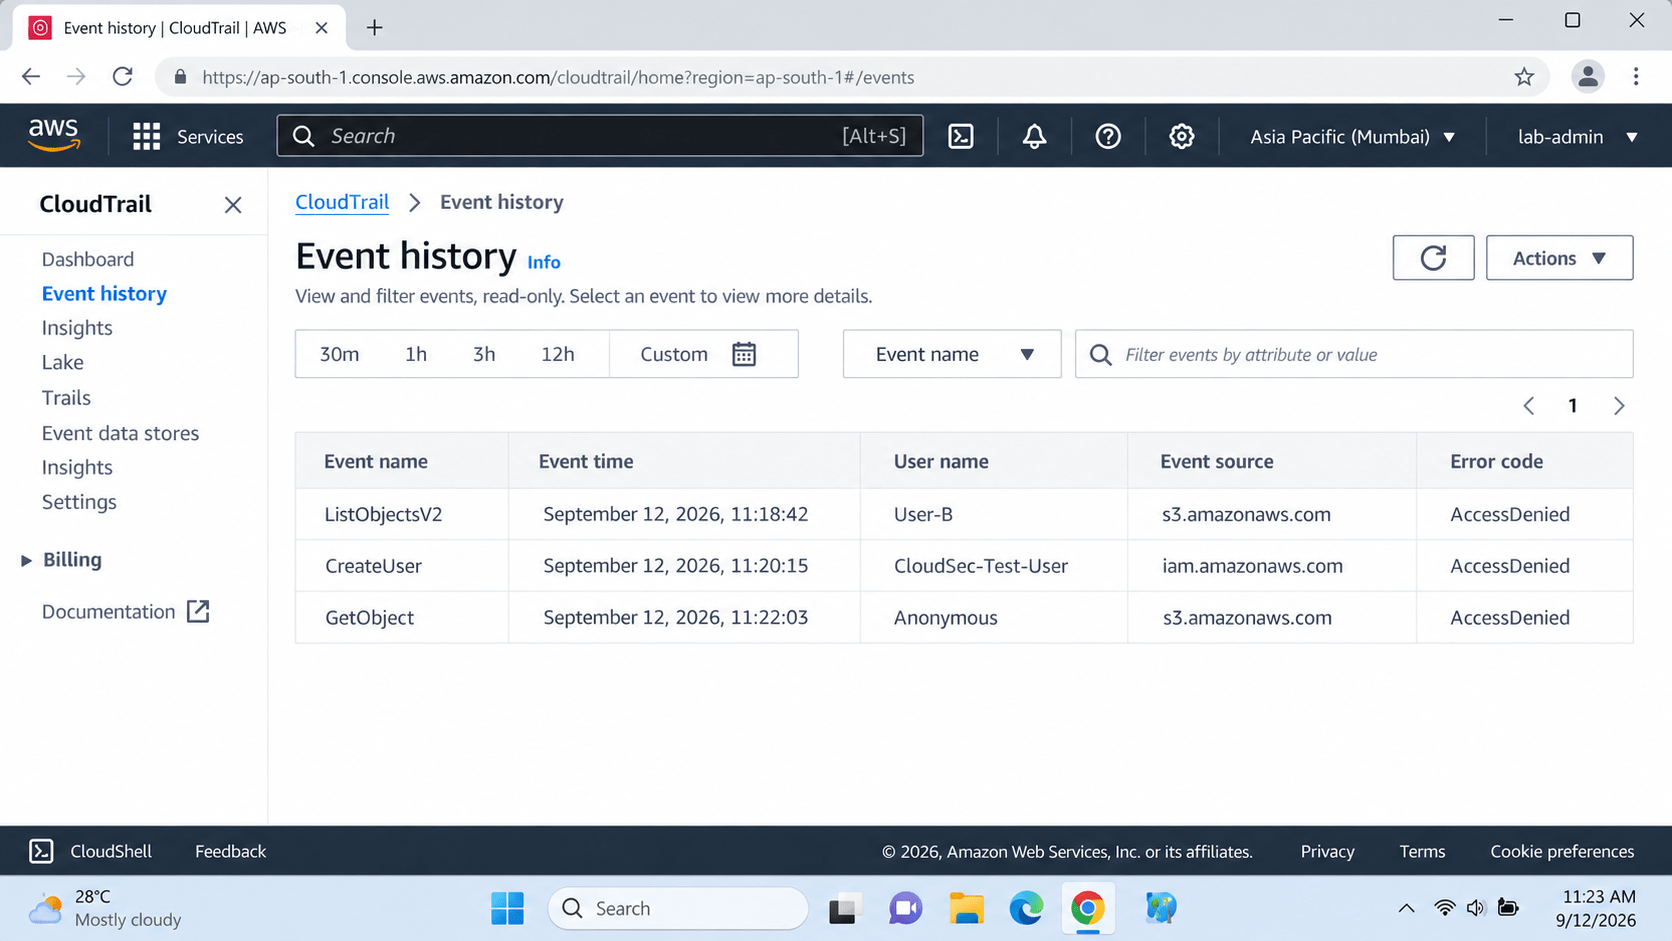
Review the cloud logs
6
Confirm that unauthorized actions are denied
Example :
Task 6: Document the Attack and Defense
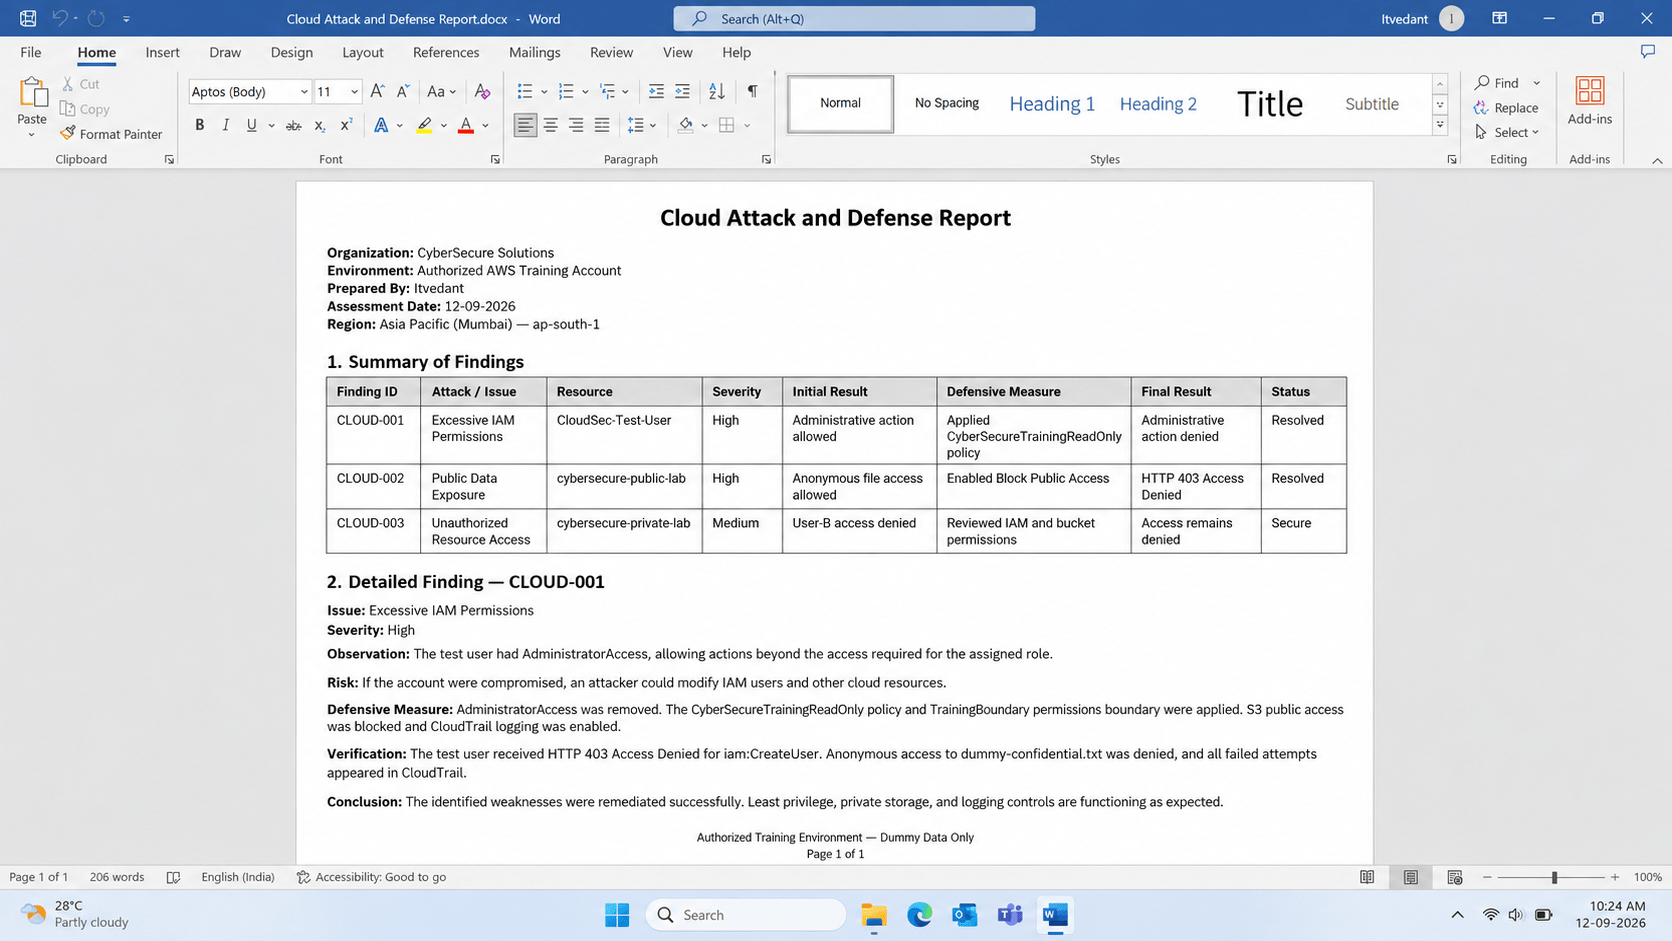
Record what happened before and after applying the security controls
For each vulnerability, record:
Example :-
| Field | Example |
|---|---|
| Finding ID | CLOUD-001 |
| Attack/Issue | Excessive Permissions |
| Resource | Test IAM User |
| Severity | High |
| Initial Result | Unauthorized action allowed |
| Defensive Measure | Least-privilege policy |
| Final Result | Unauthorized action denied |
| Status | Resolved |
Example :-
Great job!
You have successfully completed your first lab on Cloud Security Attack Simulation and Defense.
In this lab, you have: Simulated basic attacks in an authorized cloud environment, Identified security weaknesses, Applied appropriate defensive measures, and Verified that the implemented security controls prevented the attacks from succeeding.
Checkpoint
By Content ITV